Ethical Hacking Application Uses
Explore the key applications of ethical hacking, from cybersecurity and vulnerability testing to protecting networks, systems, and sensitive data from threats.
Every 39 seconds, a cyberattack hits somewhere in the world. By 2026, the global cost of cybercrime is projected to surpass $10.5 trillion annually, a number that is larger than the GDP of most countries combined. Yet, there are not enough skilled professionals to stop it.
Here is what that means for you as a student or fresher: the cybersecurity talent gap currently stands at over 3.5 million unfilled positions worldwide. Organizations are not just looking for anyone; they are actively searching for individuals who understand how attackers think and know which tools to use to stop them.
This is exactly where ethical hacking applications come in.
Ethical hacking is no longer a niche skill; it is a core professional requirement. Every organization that operates online needs people who can find vulnerabilities before attackers do. That is exactly what ethical hacking applications make possible.
The cybersecurity window is open right now, but it won't stay that way. Students and freshers who start learning ethical hacking tools today are the ones landing interviews, clearing certifications, and stepping into six-figure roles tomorrow. The question isn't whether this field is worth it. The question is whether you'll move fast enough to claim your spot.
This blog breaks down every major category of ethical hacking applications: what each tool does, how professionals use it in real-world attack and defense scenarios, and exactly what skills you need to work with them confidently and credibly.
What Is an Ethical Hacking Application?
An ethical hacking application is a software tool used by cybersecurity professionals to legally test and identify security weaknesses in systems, networks, and applications. It helps simulate real hacker attacks in a safe and controlled way so that vulnerabilities can be discovered and fixed before they are exploited.
Key points:
-
Used with proper authorization: These applications are used only after permission from the organization or system owner, ensuring all activities are legal, ethical, and controlled.
-
Detects security vulnerabilities: They help uncover weaknesses such as weak passwords, outdated software, misconfigurations, and exposed services that could be targeted by attackers.
-
Simulates real-world attacks safely: Ethical hacking tools replicate hacker techniques in a controlled environment to show how a system could be compromised without causing actual damage.
-
Supports penetration testing: These tools are widely used in security assessments to test system resilience and improve overall cybersecurity defenses.
-
Widely used in the cybersecurity industry: Ethical hacking and penetration testing are standard practices in organizations because over 70% of companies prioritize regular security testing to reduce cyber risk.
Why Ethical Hacking Applications Matter More Than Ever in 2026
Ethical hacking applications are becoming essential in today’s digital world because cyber threats are growing faster than ever. In 2026, global cyberattacks increased by nearly 38%, and this upward trend continues into 2026, making security testing a top priority for organizations. These tools help companies identify and fix vulnerabilities before attackers can exploit them, reducing major financial and data risks.
Key points:
-
Rising cyberattacks worldwide: Cyber threats have increased significantly, with attacks growing by around 38% in 2023, showing how quickly the digital risk environment is expanding.
-
Shift to proactive security: More than 60% of organizations now focus on proactive security testing using ethical hacking tools instead of waiting to respond after an attack happens.
-
High cost of data breaches: The global average cost of a data breach reached about $4.88 million in 2024 (IBM report), making prevention through ethical hacking extremely important.
-
Growing threat in India: India recorded over 1.4 million cybersecurity incidents in 2023, with sectors like finance and healthcare being heavily targeted.
-
Increased job demand for practical skills: In 2026, employers prefer candidates who can work with real ethical hacking tools and perform hands-on security testing rather than only having theoretical knowledge.
Major Ethical Hacking Applications and Their Real-World Uses
Ethical hacking applications are cybersecurity tools used to legally test systems, networks, and applications. They simulate real cyberattacks in controlled environments to identify vulnerabilities before attackers exploit them. Cybersecurity is increasingly important because global cyberattacks rose by nearly 38% in 2023, and average data breach costs reached $4.88 million.
1. Penetration Testing Applications
Penetration testing applications simulate real attacks to identify exploitable vulnerabilities in systems and applications. They help organizations understand real attack impact and improve overall cybersecurity defenses effectively.
Tools:
-
Metasploit: Metasploit provides exploit modules that allow ethical hackers to simulate real-world attacks on systems effectively.
-
Core Impact: Core Impact enables advanced penetration testing with automated exploitation and detailed enterprise-level security reporting features.
-
Burp Suite Professional: Burp Suite Professional acts as an intercepting proxy, allowing testers to analyze and modify web requests.
2. Vulnerability Scanning Applications
Vulnerability scanning tools automatically detect system weaknesses like missing patches, outdated software, and misconfigurations. Over 60% of of organizations use proactive scanning to reduce cyber risks effectively.
Tools:
-
Nessus: Nessus scans systems using extensive vulnerability databases to detect known security issues and weaknesses quickly.
-
OpenVAS: OpenVAS is an open-source vulnerability scanner identifying network and system weaknesses for security assessment purposes.
-
Qualys: Qualys provides cloud-based continuous vulnerability scanning and compliance monitoring for enterprise cybersecurity management systems.
3. Network Monitoring and Traffic Analysis Applications
Network monitoring tools analyze traffic flow to detect anomalies, unauthorized access, and suspicious activities. Studies show that over 70% of cyberattacks involve network-level reconnaissance or exploitation phases.
Tools:
-
Wireshark: Wireshark captures and analyzes live network packets to identify suspicious activity and protocol communication details.
-
Tcpdump: Tcpdump captures network traffic using a command-line interface for detailed server-based network analysis and troubleshooting.
-
Nmap: Nmap discovers hosts, open ports, and services running on networks for reconnaissance and mapping purposes.
4. Web Application Security Testing Applications
Web application security tools identify vulnerabilities like SQL injection, XSS, and authentication flaws. OWASP reports these among top global application security risks consistently.
Tools:
-
Burp Suite: Burp Suite intercepts HTTP requests between browser and server allowing detailed security testing and analysis.
-
OWASP ZAP: OWASP ZAP automates web vulnerability scanning and integrates security testing into development workflows efficiently.
-
SQLmap: SQLmap detects and exploits SQL injection vulnerabilities in database-driven web applications automatically and effectively.
5. Password Security Testing Applications
Password testing tools evaluate authentication strength using brute force, dictionary, and hybrid attack techniques. Over 80% breaches involve weak or stolen credentials globally.
Tools:
-
John the Ripper: John the Ripper performs password cracking using dictionary and brute-force methods for credential testing.
-
Hashcat: Hashcat uses GPU acceleration to crack password hashes at extremely high speeds for security analysis.
-
Hydra: Hydra performs automated login attacks across multiple services like SSH, FTP, and HTTP protocols.
6. Wireless Network Security Testing Applications
Wireless security tools analyze Wi-Fi networks for weak encryption, rogue devices, and configuration vulnerabilities. Wireless attacks are common due to insecure network setups.
Tools:
-
Aircrack-ng: Aircrack-ng captures wireless packets and tests Wi-Fi encryption strength to identify security vulnerabilities effectively.
-
Kismet: Kismet detects hidden networks and rogue access points for wireless monitoring and intrusion detection systems.
-
Reaver: Reaver exploits WPS protocol vulnerabilities in wireless routers to test network security configurations thoroughly.
7. Malware Analysis Applications
Malware analysis tools examine malicious software behavior in isolated environments to understand attack patterns. Ransomware incidents continue increasing globally causing significant financial damages annually.
Tools:
-
Cuckoo Sandbox: Cuckoo Sandbox executes malware in isolated environments and monitors system behavior and network activity.
-
IDA Pro: IDA Pro performs advanced reverse engineering to analyze malware code structure and execution logic deeply.
-
Ghidra: Ghidra provides open-source reverse engineering capabilities for analyzing malware binaries and software security research.
8. Phishing Simulation Applications
Phishing remains one of the most common attack methods, responsible for over 90% breaches. These tools help organizations improve employee awareness and security resilience.
Tools:
-
GoPhish: GoPhish creates realistic phishing campaigns to test employee awareness and response to malicious emails.
-
King Phisher: King Phisher tracks phishing engagement and generates detailed reports for improving security awareness training.
-
Social Engineering Toolkit: Social Engineering Toolkit simulates phishing and social engineering attacks for security testing and awareness training.
9. Forensics and Incident Response Applications
Digital forensics tools investigate cyber incidents by recovering evidence and analyzing system activity. They help organizations understand attacks and support incident recovery processes effectively.
Tools:
-
Autopsy: Autopsy analyzes disk images and recovers deleted files for forensic investigation and analysis purposes.
-
Volatility: Volatility examines memory dumps to detect hidden processes, malware, and system-level forensic evidence.
-
FTK (Forensic Toolkit): FTK provides comprehensive forensic analysis tools for evidence collection and cyber incident investigations.
10. Operating Systems for Ethical Hacking
Ethical hacking operating systems provide pre-installed tools for penetration testing and cybersecurity analysis. They offer complete environments for security professionals and researchers.
Tools:
-
Kali Linux: Kali Linux is a penetration testing operating system with hundreds of pre-installed security tools.
-
Parrot OS: Parrot OS is a lightweight security-focused operating system used for ethical hacking tasks.
-
BlackArch Linux: BlackArch Linux provides an advanced penetration testing distribution with extensive security tools for professionals.
How Ethical Hacking Applications Are Used in Different Career Roles
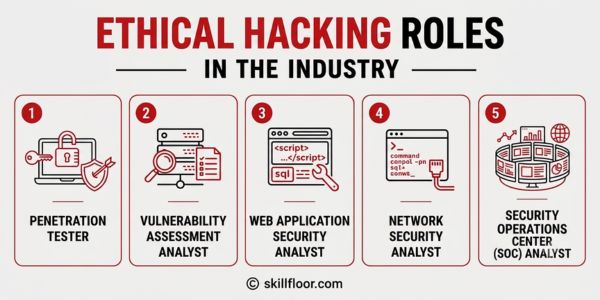
Ethical hacking applications are used differently across cybersecurity roles based on job responsibilities and focus areas. Each role requires specific skills to detect vulnerabilities, monitor systems, and perform security testing. Understanding these roles helps learners choose the right cybersecurity career path and build strong technical expertise.
Key points:
-
Penetration Tester: Simulates real-world cyberattacks to find system and application vulnerabilities. Entry-level salary in India ranges from ₹4–₹8 LPA, increasing with experience and certifications.
-
Vulnerability Assessment Analyst: Identifies and reports security weaknesses without exploiting them. Salary generally ranges from ₹5–₹10 LPA depending on experience and company size.
-
Web Application Security Analyst: Secures web applications by detecting issues like injection flaws and authentication vulnerabilities.
-
Security Operations Center (SOC) Analyst: Monitors systems in real time to detect and respond to cyber threats using security tools and platforms. It is a common entry-level cybersecurity role.
-
Cybersecurity Consultant: Works across multiple security areas to assess risks and recommend security improvements for organizations. Requires strong technical and communication skills.
What Skills Do You Actually Need to Work With These Tools?
|
Skill Area |
Explanation |
|
Networking Fundamentals |
Understand TCP/IP, ports, protocols, and basic network traffic flow for tools like Nmap and Wireshark. |
|
Operating System Proficiency |
Linux knowledge is essential for using most ethical hacking tools and command-line operations. |
|
Scripting and Programming Basics |
Basic Python helps automate tasks, customize tools, and understand simple security issues. |
|
Security Concepts and Frameworks |
Knowledge of OWASP Top 10, penetration testing stages, and CVSS helps structured security analysis. |
|
Documentation and Reporting |
Writing clear reports is important for communicating vulnerabilities and security findings effectively. |
How Hands-On Training Connects Theory to Real Application
Hands-on training is essential in ethical hacking because real skills develop through practical tool usage, not theory alone. It helps learners understand real attack scenarios and build job-ready cybersecurity experience. Structured programs also simulate real industry environments to improve confidence and technical ability.
Key points:
-
Hands-on training bridges theory and real-world ethical hacking applications through practical experience.
-
Live labs help learners use tools like Kali Linux, Wireshark, and Metasploit effectively.
-
Skillfloor’s Certified Ethical Hacking Course provides structured, project-based learning with real cybersecurity tools.
-
Individual project work builds practical experience and strengthens job-ready cybersecurity skills.
-
Practical training improves employability by preparing learners for real industry security challenges.
Career Outlook for Ethical Hacking Professionals in 2026
The career outlook for ethical hacking professionals in 2026 is strong due to swift digital growth and rising cyber threats. Organizations are increasing investments in cybersecurity to protect systems and data. This has created consistent demand for skilled ethical hacking professionals in India and worldwide.
Key points:
-
Growing cybersecurity market: India’s cybersecurity market is projected to reach $13.6 billion by 2025, growing at over 15% Annual growth rate.
-
Rising digital adoption: Government initiatives like Digital India and increased cloud usage are driving demand for security professionals.
-
High talent gap: NASSCOM estimates India needs over 1 million cybersecurity professionals, creating strong opportunities for freshers.
-
Salary growth: The average cybersecurity salary in India is around ₹1,000,000 per year, depending on role, skills, and experience level.
-
Wide career flexibility: Ethical hackers are hired across BFSI, healthcare, IT, and e-commerce, with growing remote and freelance opportunities.
FAQ's
1. What is the difference between an ethical hacking application and regular software?
Ethical hacking applications are used for authorized security testing and vulnerability detection. Regular software is used for general tasks, while hacking tools focus on security assessment and protection.
2. Do I need programming skills to use ethical hacking tools?
Basic scripting knowledge, like Python or Bash, is helpful, but not always required. Many tools have user-friendly interfaces for beginners to start learning effectively.
3. Which ethical hacking tool should I learn first as a beginner?
Start with Nmap for network scanning and Wireshark for traffic analysis. These build a strong foundation before moving to advanced tools like Metasploit and Burp Suite.
4. Is Kali Linux necessary for ethical hacking?
Kali Linux is not mandatory, but it is widely used in training and industry. It comes preloaded with tools, making it easier for learning and practice.
5. Are there legal restrictions on using ethical hacking applications?
Yes, using ethical hacking tools without permission is illegal. All security testing must be authorized and follow legal guidelines under cybersecurity laws.
6. Which certifications validate ethical hacking skills for employers?
Popular certifications include CEH, OSCP, and CompTIA Security+. These are widely recognized by employers in the cybersecurity and IT industries.
Ethical hacking applications are essential tools that help organizations identify, prevent, and respond to cyber threats in an increasingly digital world. For students and freshers, gaining practical knowledge of these tools is a key step toward building a strong and future-ready cybersecurity career. With growing demand, competitive salaries, and expanding job opportunities across industries such as IT, BFSI, healthcare, and government, ethical hacking offers a highly promising career path for skilled professionals. Continuous learning, hands-on practice, and real project experience are what transform basic understanding into true industry readiness.
Sources Referred to:
1. The global average cost of a data breach reached 4.4 million - https://www.ibm.com/reports/data-breach
2. Cybersecurity salary in India is around ₹1,000,000 - https://www.geeksforgeeks.org/cyber-security-salary/
Digital Marketing Courses in Other Locations in India
Ahmedabad | Aurangabad | Bangalore | Bhilai | Bhopal | Bhubaneshwar | Chandigarh | Chennai | Cochin | Coimbatore | Dehra Dun | Delhi | Faridabad | Ghaziabad | Gorakhpur | Guntur | Gurgaon | Guwahati | Hyderabad | Jaipur | Kanpur | Khammam | Kolkata | Lucknow | Madurai | Mumbai | Mysore | Nagpur | Noida | Patna | Pondicherry | Pune | Ranchi | Shimoga | Surat | Thane | Thiruvananthapuram | Tiruchirappalli | Tirupati | Vadodara | Visakhapatnam | Warangal | Jalandhar | Jodhpur | Indore | Durgapur | Jamshedpur | Dhanbad | Kota | Karnal | Udaipur | Amritsar | calicut | Nashik | Ludhiana | varanasi | thrissur | Mangalore | Raipur |
-
 haqnawazgood applicatoin